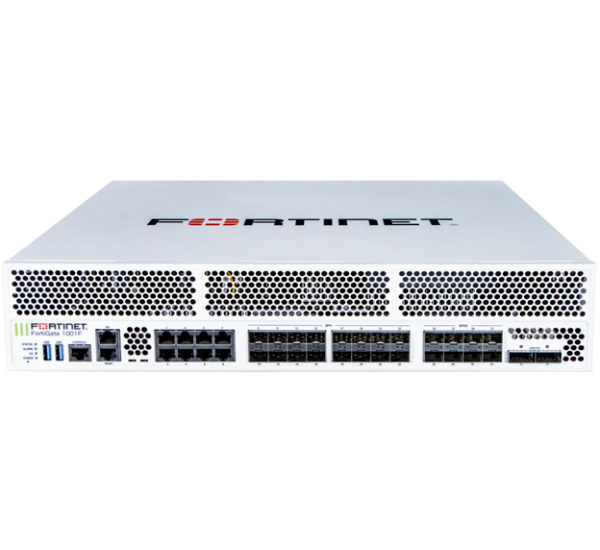
The FortiGate 1000F is a high-end, 2RU next-generation firewall (NGFW) that sits near the top of the "F-Series" portfolio. It is engineered for large-scale data centers, internet gateways, carrier networks, and service providers that require massive throughput, extensive 100G connectivity, and the ability to enforce security policies on enormous volumes of traffic. This model represents a significant step up in raw power and port density from the 600F.
Key Features and Capabilities
The 1000F is built for scale, performance, and reliability in the most critical network positions.
Massive NP7 & CP9 Processing Power: Leverages multiple, high-capacity Fortinet NP7 (Network Processor) and CP9 (Content Processor) chips. This provides unparalleled hardware acceleration for networking and security functions, making it capable of inspecting encrypted traffic at a scale that software-based solutions cannot match.
High-Density 100G Connectivity: A defining characteristic is its extensive number of 100 Gigabit Ethernet (100GE) ports. This makes it suitable for high-speed data center spines, internet peering points, and as an aggregation firewall for multiple lower-tier firewalls.
Carrier-Class High Availability & Redundancy: Features redundant, hot-swappable power supplies and fans. It supports advanced high-availability modes, including Active-Active clustering and FGSP (FortiGate Session Life Protocol), for stateful failover in the largest deployments.
Integrated Solid-State Drive (SSD): Includes built-in SSD storage for local logging and analytics, which is essential for compliance, forensics, and debugging in environments where the volume of logs would be overwhelming for external systems alone.
Massive Scale for Sessions and VDOMs: Engineered to handle tens of millions of concurrent sessions and supports a very high number of Virtual Domains (VDOMs), making it ideal for large Multi-Service Service Providers (MSSPs) and hyper-segmented enterprises.